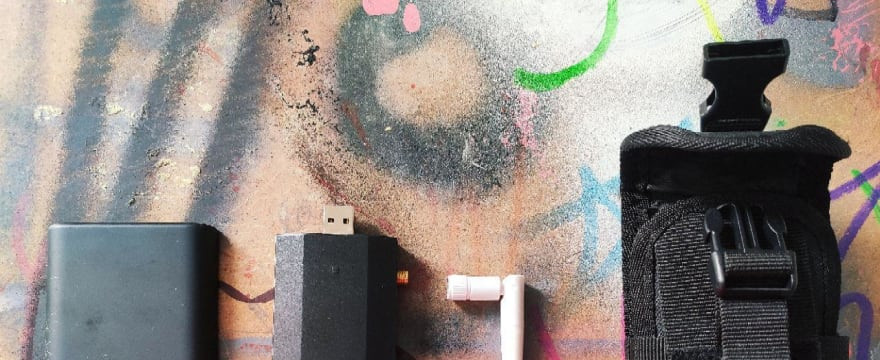Jekyll2023-03-08T00:56:40+01:00https://old.interferencias.tech/feed.xmlInterferenciasAsociación ciberactivista en defensa de la privacidad en Internet y los derechos digitales promoviendo el uso de software libre. Seguridad informática para la reivindicación.Interferenciasinfo@interferencias.techPublicados los vídeos de esLibre 20212021-11-02T00:00:00+01:002021-11-02T00:00:00+01:00https://old.interferencias.tech/2021/11/02/videos-eslibre2021
Ya están disponibles los vídeos de nuestra sala "Derechos Digitales y Privacidad en Internet + Soberanía Digital en las Aulas (Fuera Google)" de esta edición de esLibre: podéis encontrarlos junto con el resto de vídeos de esta edición en Wikimedia Commons.
Aunque también podeis encontrarlos con todo detalle de información en la página correspondiente que creamos aquí, así que simplemente os dejamos un enlace allí para que podáis echarle un ojo.
]]>Germángermaaan@interferencias.techEnvío de propuestas para la sala “Derechos Digitales y Privacidad en Internet + Soberanía Digital en las Aulas (Fuera Google)”2021-04-07T00:00:00+02:002021-04-07T00:00:00+02:00https://old.interferencias.tech/2021/04/07/eslibre2021
Otro año más volvemos a sumarnos a colaborar en la organización de otra edición de esLibre y proponer una sala para el programa de la misma. Este año, a diferencia de los anteriores, estamos buscando centrarnos más en las temáticas de derechos digitales y privacidad en Internet.
También queremos intentar organizar algunas actividades que pongan el foco sobre el problema de la continua "invasión" por parte de las grandes compañías de Internet en el funcionamiento de las aulas de escuelas e institutos, algo que se ha visto acrecentado enormemente por la situación sanitaria actual y que sin duda le ha dado todavía más poder a empresas de conocida y cuestionable ética como Google.
Si tienes algo que decir sobre algunos de estos temas, ¡no dudes en mandarnos cualquier propuesta! Los formularios de envío puedes encontrarlos en la página que hemos añadido con toda la información:
]]>Germángermaaan@interferencias.techPublicados los vídeos de esLibre 20202020-11-30T00:00:00+01:002020-11-30T00:00:00+01:00https://old.interferencias.tech/2020/11/30/eslibre2020
Ya os comentamos que este año dada la situación actual no pudimos celebrar las JASYP, pero eso no impidió organizar algo en su lugar. Aprovechando que la edición de este año de esLibre se realizó de forma online, organizamos una sala sobre Derechos Digitales, Privacidad en Internet y Seguridad Informática.
Todos los detalles ya los explicamos en su página correspondiente, así que simplemente os dejamos un enlace allí para que podáis echarle un ojo.
]]>Germángermaaan@interferencias.techSala esLibre 2020&#58 Derechos Digitales, Privacidad en Internet y Seguridad Informática2020-08-15T00:00:00+02:002020-08-15T00:00:00+02:00https://old.interferencias.tech/2020/08/15/eslibre2020
Desde Interferencias siempre nos gusta colaborar en iniciativas que nos parecen interesantes, y es por eso que tanto el año pasado como este año estamos colaborando en la organización de esLibre: un encuentro de personas interesadas en el conocimiento y la difusión del las tecnologías libres y cultura abierta. Concretamente la edición de este año será totalmente online los días 18 y 19 de septiembre, coincidiendo con el "Software Freedom Day" (que además, también es el cumpleaños oficioso de Interferencias 🌚).
Como ya sabréis, este año finalmente no pudimos realizar nuestras JASYP '20 debido a la situación actual, y ya que todos los años planteamos las Jornadas como una celebración donde compartir experiencias y conocimiento con la espontaneidad del trato en persona decidimos que no tendría sentido celebrarlas de forma online porque perdería su significado; no se trata de ser otro congreso, se trata de ser una experiencia aprovechando todo lo que nos brinda Granada.
Por todo esto que comentamos, finalmente hemos decidido presentar una propuesta de sala dentro del programa de esLibre para seguir llegando a tanta gente como sea posible. En un momento en el que las grandes compañías tecnológicas se frotan las manos pensando en todo el beneficio que podrán sacar de nuestros datos o el peligro que puede entrañar la tecnología más inocente del mundo si se le da usos con objetivos cuestionables (o peor, inconscientes), es más necesario que nunca disponer del conocimiento sobre cómo funcionan las tecnologías que está tan integradas en nuestro día a día que nos rodean de forma casi inapreciable.
Hoy más que nunca debemos ser conscientes de la necesidad de proteger nuestra privacidad y nuestra soberanía digital: tenemos que saber QUÉ tenemos a nuestra disposición y CÓMO podemos actuar; y esto, sin duda alguna, es algo que viene de la mano del Software Libre.
El planteamiento del contenido será muy parecido al que hacemos en las JASYP, pero con un formato distinto:
esLibre 2020: "Derechos Digitales, Privacidad en Internet y Seguridad Informática"
Viernes 18 de septiembre
12:30-12:40 Presentación 'Sala Derechos Digitales, Privacidad en Internet y Seguridad Informática'
Germán Martínez: Ingeniero informático, activista por los derechos digitales y el software libre, coordinador en Interferencias y LibreLabGRX y parte del equipo de organización de esLibre.
12:40-13:10 Herramientas para mantener tu privacidad en Internet
Pablo Castro: activista del software libre y la libertad en Internet. Forma parte de la asociación Trackula y se encarga de Techtopias, una newsletter quincenal sobre privacidad, soberanía digital y libertad en internet para estar al día de las noticias mas interesantes de este mundillo.
En pleno 2020, muchas grandes empresas tecnológicas basan su modelo de negocio en vender nuestra vida privada, nuestra forma de ser, qué vamos a ser en el futuro, llegando incluso a manipularnos.
En esta charla veremos rápidamente los peligros a los que se enfrenta la sociedad tecnológica actual y qué herramientas podemos tener e instalar de forma sencilla para intentar reducir la información que generamos a diario y así luchar por preservar nuestra privacidad.
13:10-13:45 Self Sovereign Identity: identidad bajo el control de las personas
Jorge Cuadrado: investigador en ciberseguridad en el laboratorio de innovación de BBVA Next Technologies. Estudió Ingeniería Informática en la Universidad de Valladolid (UVA) y el Máster en Ciberseguridad de la Universidad Carlos III de Madrid (UC3M). Ha participado como ponente en múltiples congresos como: Cybercamp, RootedCon, Hack In The Box, X1RedMásSegura o JASYP. Sus focos de interés, sobre los que siempre tiene algún proyecto en marcha, son: privacidad, impresión 3D y electrónica.
Self Sovereign Identity (SSID) es un sistema de identificación que ha surgido recientemente y que, conceptualmente, cambia significativamente respecto a modelos más tradicionales de identificación.
Mediante este esquema, las personas adquieren la responsabilidad de gestionar cómo y en qué cantidad se usan sus datos personales. Para ello, permite crear “tarjetas de identidad” digitales que pueden ser generales para cualquier servicio o específicas para cada caso. Pero… ¿qué ventajas y peligros hay detrás de SSID?
16:00-16:25 ¿Existe vacuna para los sesgos en las inteligencias artificiales?
Los humanos tenemos sesgos y parece que las máquinas inteligentes también, pero, ¿se trata esto de una feature o de un bug?
En esta charla veremos qué son las llamadas inteligencias artificiales y qué son los sesgos, por qué es tal fácil que permeen en el software, cuál es su impacto y qué podemos hacer para detectarlos y mitigarlos.
16:25-16:40 Fact-checking y fake news: caja de herramientas ciudadana para la verificación
Javier Cantón: sociólogo y comunicador audiovisual. Doctor en Ciencias Sociales, ha impartido docencia en las Universidades de Jaén, Granada, UNIR, Girona y UOC, así como diversos talleres y colaboraciones sobre pensamiento visual y visualización de datos. Investiga sobre desigualdad, redes sociales, visualidad y, más recientemente, desinformación y fake news, tema sobre el que ha elaborado material docente para una asignatura universitaria. Actualmente trabaja en Medialab UGR, coordinando RadioLab UGR entre otros proyectos, e imparte docencia en UNIR y UOC.
Saturados de información y desconfianza, resulta cada vez más complicado discernir la información cierta de la falsa. La proliferación de las denominadas fake news está reconfigurando la esfera pública y los cauces de formación de la opinión pública, lo que supone un reto para nuestras democracias, que se fundamentan en el acceso a una información veraz para sus ciudadanos.
En este taller aprenderás diferentes métodos y herramientas libres para verificar la procedencia de una noticia y luchar contra las fake news y los bulos.
16:40-17:15 Social Justice Code Repositories
Lorena Sánchez: Consultora de seguridad y cumplimiento en ElevenPaths. Jurista y politóloga por la Universidad Carlos III de Madrid. Máster en Gobierno de las Telecomunicaciones por la London School of Economics. Especialista en Derecho Tecnológico e Informática Forense. Editora del medio de análisis político y social Polikracia. Ha centrado su carrera profesional en la seguridad en organizaciones, aunque está especializada en derecho tecnológico, protección de datos, seguridad informática y su relación con las ciencias sociales y el derecho. En este sentido, investiga la interrelación entre política y tecnología desde distintos planos como los derechos fundamentales, la privacidad o las relaciones internacionales. Algunos de sus proyectos versan sobre infraestructuras críticas y seguridad internacional; seguridad y privacidad en sistemas de voto electrónico o la concepción de la privacidad en el plano social.
¿Garantiza el software libre que el usuario sea libre? ¿Son necesarios y suficientes los principios del FSM para garantizar la justicia? ¿Cuál es el rol de los repositorios de código en la promoción de la justicia en el software? Estas son algunas de las preguntas que intentaremos desgranar en la charla con el propósito principal de analizar bajo qué condiciones el Free Software Movement funciona para alcanzar la justicia en la producción, uso y consumo de software. Así, la base de la charla será retar el funcionamiento de las tesis de Richard Stallman como teoría, poniendo en valor el rol de los repositorios de código abierto y buscando los puntos débiles que deben ser mejorados.
Si bien la charla presenta un punto de vista teórico, pretende ponerle sentido al FSM a través de diferentes teorías de la justicia preguntándose cómo el FSM puede ser clave en la libertad del usuario sin quedarse en papel mojado.
17:30-17:55 Software Libre para las personas
Paula de la Hoz: Co-fundadora de Interferencias. Senior Red Team en Telefónica Ingeniería de Seguridad.
Desde su origen, el Software Libre está ligado a la comunidad, a ser partícipe de proyectos con el ánimo de que lleguen a otras manos, las que sean, y sigan mejorando.
En la actualidad, desde asociaciones hasta grupos de vecinos se enfrentan a diario a un mundo ya protagonizado por la tecnología, y es aquí donde el software libre debería ser una herramienta esencial que defienda los intereses de las personas sin que ello suponga ceder seguridad y privacidad.
En esta charla pretendo presentar las posibles soluciones libres para las necesidades de asociaciones y otras comunidades, entre ellas BarrioCheck, un proyecto para alertas de barrios basado en OSM que desarrollé hace poco y que pretende dar comienzo en Madrid.
Durante la charla pretenden cubrirse los siguientes temas: comunicación segura y libre, hardening básico e introducción a sysadmin de comunidades, instrucciones y recursos para nivel de usuario para miembros no técnicos, BarrioCheck, hardware y software libre para centros/bibliotecas/radios sociales; entre otros.
17:55-18:20 Hacktivismo no es nombre de señora
Sofía Prósper: Defensora de la privacidad, arquitecta e ilustradora. Forma parte de la asociación Trackula y actualmente se encuentra construyendo IUVIA, ambos proyectos centrados en la defensa de la privacidad en Internet.
Viviendo el año más extraño de nuestras vidas, este atípico 2020 nos deja con nuestros derechos digitales afectados y con unos precedentes en solucionismo tecnológico que nadie hubiera imaginado si una pandemia no los hubiera instaurado velozmente.
El capitalismo de la vigilancia es sólo un síntoma de un sistema económico y político funcionando como se espera. Por eso es el momento idóneo para movernos, para investigar, para estar informadas y no parar de defender nuestras libertades antes de que la tecnología ‘nos venga a salvar’.
En esta charla nos gustaría, a parte de hacer una pequeña introducción de cuál es el estado actual de las cosas, mostrar proyectos e iniciativas que no se han rendido al ‘yo no tengo nada que esconder’ y siguen al pie del cañón llegando cada día a más gente.
18:20-18:45 ¿Hacia un feudalismo de los datos?¿Derecho o tecnología?¿Cómo defendernos?
Luis Fajardo: de perfil claramente universitario, ha sido juez y abogado. Fue responsable de las redes de la Facultad de Derecho de la UAM en los años 90, siendo becario de Formación de Profesorado Universitaario (FPI/FPU). Ha impartido docencia en las Universidades Autónoma de Madrid, Almería, Gerona, UNED y La Laguna, donde lo sigue haciendo en la actualidad, adscrito al Área de Derecho civil. Ha sido fundador de varias aociaciones, entre ellas el Centro de Alternativas Legales, y miembro de Madrid Wireless, el Grupo de Usuario Linux de Canarias (GULiC), Secretario de ESLIC (Empresas de Software Libre de Canarias), y la Oficina del Software Libre de la ULL, con la que viene colaborando desde hace muchos años. Desde 1999 usa exclusivamente GNU/Linux en sus sistemas. Mantiene y administra diversos nodos del Fediverso, como https://encanarias.info (Diaspora) y Silba.Me (Mastodon).
La Administración está llena de malas prácticas, el mercado está dirigido a primar la corporocracia, que está sustituyendo a la democracia.
El Fediverso, las redes federadas, y los servicios libres (que pueden ser instalados “on premise”), pero no parecen suficientes. Realmente tenemos normas que intentan limitar el avance de la corporocracia, fundamentalmente el RGPD. Lamentablemente no se está usando, y debe lanzarse un aviso a navegantes.
Cómo nos enganchan: dispositivos que no obedecen a sus dueños, redes sociales que polarizan, manipulación informativa e información individualizada…
Cómo defenderse: elección de los servicios con unos parámetros técnicos (arranque libre, open source, interoperable, estándar y federado…) y jurídicos (que permite exigir aquellos criterios técnicos, básicamente, RGPD).
#somosruido 💻✊📣
JASYP '17JASYP '18JASYP '19]]>Germángermaaan@interferencias.techSafety on the streets with Python2020-07-23T00:00:00+02:002020-07-23T00:00:00+02:00https://old.interferencias.tech/2020/07/23/safety-on-streets-python
For a few years I’ve been thinking in ways tech could help neighbourhoods into becoming more safe taking advantage of the people collaboration. It first came to me after realizing a neighbour a loved in my home town had some communication problems with the essential services. The whole idea of mine is logistically difficult to perform as so I ended up just theorising for a long time without actually writing a single line of code for that idea. Recently, after a discussion in Mastodon, I realized there are some tiny goals to make public spaces safer and that we could start from there.
I’ve been curious about Open Street Map for a while, so I decided I could work in my spare time between projects in a simple python code that created a OSM with marks. The whole idea was to create a launching portal (static, at first) with a map-launching button, and the map contains marks with dangers around the neighbourhood. The warnings could be from to broke asphalt to unsafe LBGTIQ spaces. Or! in a more positive sight, safe spaces! (safe LBGTIQ shops and meeting points, feminist friendly spaces, etc) as well as identifying trigger spaces such as betting places/alcohol stores. It kind of depends on the needs of each neighbourhood. It only needs a JSON (there’s an example already) where you have to set location and the advise.
The idea is for the people to be able to upload information through email or hashtags, some people already suggested to add a form and some of them are planning on merge request that option. I’m so happy about how many people from my city wanted to help as soon as I launched the repo and I decided to share it here in case you guys want to use it in your neighbourhoods as well, or in any case modify the repo.
Have fun and stay safe! I believe in the collaboration of the people for creating safer cities.
Right now it’s in Spanish, as I thought it would help local groups to better understand it, but I hope to soon add the English translation.
]]>Paulainversealien@protonmail.comSocial Engineering&#58 The performance security2020-07-10T00:00:00+02:002020-07-10T00:00:00+02:00https://old.interferencias.tech/2020/07/10/social-engineering-performance-security
Disclaimer: All of the following information takes for granted you’ve been hired for it.
One of the best parts of offensive security is the wide range of attacks than can be performed. As the idea is to simulate a real cyberattack, there are several kind of things to do to approach the “victim”. Even most of it involves using various tools in the computer, it also implies physical access, phishing, and getting information though the users of the system. This parts involves a bit of a performance, to learn about what kind of people work there, what kind of clients do they have, etc. It’s helpful for either simulate being one of those or craft personalized attacks. For example, if you know that most of the staff use a specific tech brand, you can create a malicious gift (a pendrive, link, program, etc) which also requires some serious crafting, how good are you with stickers and presentation? ;)
Anyway when it comes to emulate other kind of person, there are many useful things you can use. When speaking through the phone, or in person, you need to have clear your basic information (name, age, personal details, contextual…) so first of all is building a character. The character could change depending on the situation, there are some random character generators out there, but you might want to create a more specific character.
I remember I had this job interview time ago in which saying I used to roleplay fiction with my friends was a nice flag. Since I was a kid I had to study contextual details and facial expressions for personal reasons, and apparently it came in handy for my professional development. Understanding how the people in a company works, communicate and perform is a huge tip into understanding what kind of flaws they might have. Also you have to know your limitations, as much as I would like to perform some roles, I have to contextualize my complexity, my voice and my general looks. I once asked a junior to act as my boss as he had this very strong voice, and I made myself a role as a junior (I was senior of that project) due to my soft voice, and it worked.
Investigating the people in a company includes:
Learning about their structure (do they have separates offices or do they work all together?, do they have to dress formal? do they have managers, bosses, juniors, seniors or other kind of organization?) which sometimes is just a matter of browsing Linkedin, official website and social media.
Learning about their routines (do they have breakfast at the same place everyday? do they go outside the building for that? do they know each other or rotate so they have different workmates from time to time?) This information could lead into attacks as the one Naomi Wu did in China, in which she met a guy from a company who used to have coffee in front of the company building, or use sniffing devices.
Learning about their tech (do they use windows? apple? do they bring laptops outside or the equipment is inside the building all the time?)
Learning about the clients (are they used to attend callings from clients? do they have review pages that could give us context on certain issues that happened before?) This could give you context to work with, referring to that issue plus some public information (NIF for example) could make people think you are this client for real.
Of course believing your own story is important, so if you are using a phone is wise to have a cheatsheet in front of you with your fake information, and cautiously save it for afterwards in case you are successful and you need to use that character again. For example: name, ID, age, birth place, favourite color, pet, anything that you think is needed. Even using fake sounds such as a crying baby (a very useful resource to create a hurry-up environment), a barking dog or anything like that. Creating those kind of environments could be useful for gathering information that shouldn’t be released: for example in the case I mentioned before I was a “fucked up junior” in a Friday evening (when everyone wants to finish already). Every detail is important.
Using different phone numbers also allows you to dissociate your character from your professional number. If you are perfectionist enough you can create some fake profiles beforehand in social media in order to refer to them if the chance comes. But the whole thing is more about coming up with things naturally even in the most weird situations. I read about a useful schematic into character creation for Social engineering when I was studying for readteam some years ago and the woman authoring even had rings, accessories and outfit for specific situations. Actually it’s all about how far are you willing to go. I have some friends who had to craft a pen-drive present and we laughed about being crafty enough for making it cute and passable. There’s this guy (not friend of mine, but he gave a speech about it) who even asked his mom to collaborate for an attack into a prison. Not gonna lie, the hell of a fun job.
Obviously we are not willing to cause trouble to anyone, so when we write about it afterwards we try to generally speak about the attack and don’t point at anyone. It’s important to focus on improving the security measures instead on the specific people. The idea is to afterward suggest how to improve the security methodology in the customer assistance and daily performance so everyone is at least informed into how to react against different situations. So… here you go some tips for avoid falling into this:
If a hurry up email, calling or customer appears on anyday, but even more on Friday afternoon, don’t panic, slow down and calmly try to resolve the problem.
Never ever ever discuss personal details or relevant information without letting your responsible know and NEVER through a non-safe channel. Never never change password through phone calls or anything. Even if it sounds like a really hurry-up situations. actually specially if so.
If someone you don’t know acts like is working there, be cautious with the information disclosure and don’t let this person know important details until you are referenced by other workmates. Try to train yourself into what kind of information you can and cannot disclosure. My family sometimes ask me about my job and I clearly know what I can and cannot say, not because of them, but because of who else is listening.
Careful with very cool presents at work. EXTREMELY careful with pendrives. set it ON FIRE
If you see someone putting a RPI in your Network is probably not the cleaner. Call security. (There are some workmates that had to deal with detention more than once) this person might be a friendly redteam fella, or a real attacker, in both cases you need to tell security. We will deal.
]]>Paulainversealien@protonmail.comWhy anti-encryption laws are crazy2020-06-25T00:00:00+02:002020-06-25T00:00:00+02:00https://old.interferencias.tech/2020/06/25/anti-encryption-laws-crazy
Introduction
Since tech became open and community guided, the fear of developing tools for the users and not for the companies or the government has grown bigger. In recent news a new bill is presented in which Justice Department will be able to require manufacturers of OS and devices as well as communication providers the ability to decrypt data upon request.
The whole point of encryption is to ensure the security of your information. Requiring your information to be safe is not just a matter of “hiding” stuff. Several cyberattacks push Blue Teams and companies to keep their security in its peak, backdoors are a risk to everyone’s information. An encryption with a backdoor is no longer a trustworthy encryption, it might be a hard-to-open door, that’s all. Let’s explore a bit about encryption to make sense of this:
From Diffie and Hellman to RSA
If you guys ever had a calculus or algorithms subject you might have heard these names already. Whitfield Diffie and Martin Hellman are the cryptologist that name the method for securely exchanging cryptographic keys. The whole, basic idea of this method is to create a shared key without the intervention of third parties for obvious reasons, but it had it flaws as it’s based in symmetric keys. It’s still useful for many things, but RSA was based in the same idea using asymmetric keys. I had to calculate RSA with pen and paper at university and it’s a pain in the ass, so I will shortcut and give the general recipe:
Using a couple of large prime numbers and keep them secret, using randomness, which by the way isn’t that easy, I will explain later.
The modulus for public and private keys in n is defined as part of the public key.
We involve some magic called Carmichael’s totient function and Euclidean algorithm. Using a fast duckduckgo search we can create an idea of both, but the whole point is to have a solid computable method for defining the private key so it’s a one-way calculus and there’s no way of getting it back from the information provided, in case a naughty MiTM is happening (which was a real concern in Diffie-Hellman).
Actually the main idea is to craft a modular multiplicative inverse, the main part of the private key, that can be used to resolve all, but this process is not compromised, and actually all the information used to calculate this value is disposable.
Anyway after all this gibberish, the important fact here is that we craft a double-key that can’t be decrypted using the information of the public part (the shared one) as that part is a one way-ticket.
Randomness
We previously said that creating true randomness is not that easy, right? Well randomness is an important part of the process, so let me explain. If we think of a limit from the bottom (0 for example) to the top (let’s stay classy and say 10) and you are asked to randomly choose a number you could say anything (did you think of 7? Hah I knew it) and that might be considered random but let’s remember computers are very stupid creatures that depends on clear commands to work. So “programming” randomness depend on choosing random facts so the computer can craft some randomness.
This is why when we create a public-private key using GPG we might be asked to move the mouse all around, open and close stuff and similar, the computer is trusting on your human randomness. This is safe enough for that case, but let’s think of a situation in which we need randomness and human interaction is not an option. In my case I’m thinking of an Arduino IoT project or similar. A formal, new generation computer would be able to do the work just fine, but for example in IoT we will need specific chips for encryption, mine is ATECC608A, that includes (tadah tadah) Elliptic Curve Diffie-Hellman. The idea is the same, is to perform one-way-ticket public and super safe private encryption embedded in a project. If encryption was supposed to be decrypted for anyone who commands it, do you think all this effort would be necessary?
At this point you might already think what I was trying to explain at first: encryption is designed to be unbreakable on command, it’s the whole point. Not only due to the trust in this third person, but due to the method itself. Do you see any step in the process involving “oh and create a copy key to this very trustworthy third party!” no, because it makes literally no sense in theory. It doesn’t matter how much you trust this third party, accepting these terms involves:
Compromising your security even more, as your safety not only depends on being attacked, but it also depends on you trustworthy third party being attacked.
Changing almost 25 years of hard work made by mathematicians in order to keep you safe to literally make the internet more dangerous.
So, think about this when trying to build an opinion on how important encryption is. Anything that tries to break our safety for whichever reasons have to be at least, subject of suspicion.
]]>Paulainversealien@protonmail.comGenetic algorithms for brute forcing2020-06-04T00:00:00+02:002020-06-04T00:00:00+02:00https://old.interferencias.tech/2020/06/04/genetic-algorithms-brute-forcing
Due to my work I tend to use brute force lists a lot, mostly to test incorrect login management. Sometimes I feel I get really close to correct passwords either guessing or using profiling tools. I don’t know if some of you, when it comes to change the default or old passwords you just take your old one and change it a bit. That’s mostly wrong btw.
In any case recently I felt like hand-writing customized lists out of guessing on a text file was a poorly decision, so I decided to create a command that creates fitted guessing options from a fitting range using a genetic algorithm. I created a GitLab repo in order to share it and I’d like to improve it, mostly because I know C++ might not be the best option and also because I’m open to suggestions, in general.
If you are curious please check and merge request your ideas!
Example of use with a sample guessed password and the desired fitness 2:
]]>Paulainversealien@protonmail.comYour friend and neighbour WiFi2020-03-29T00:00:00+01:002020-03-29T00:00:00+01:00https://old.interferencias.tech/2020/03/29/friend-neighbour-wifi
Recently I’ve been reading about ways to help your neighbourhood with the COVID-19 crisis, here in Spain. But one of the tips they gave was quite unsecure, because it’s based in the fact that everyone is nice: “Share your WiFi!” well, it is a wonderful idea to share your Internet connection if you know how to protect it and have different channels for you and your guests. On the other hand trusting on unknown open WiFis is also a bad idea. I want to show today why, using a Wifi pineapple.
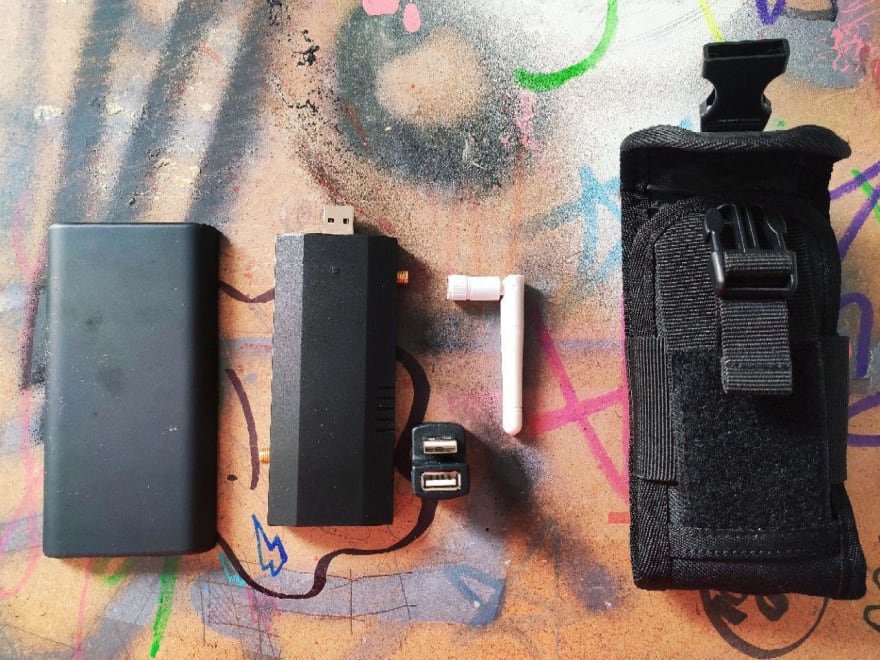
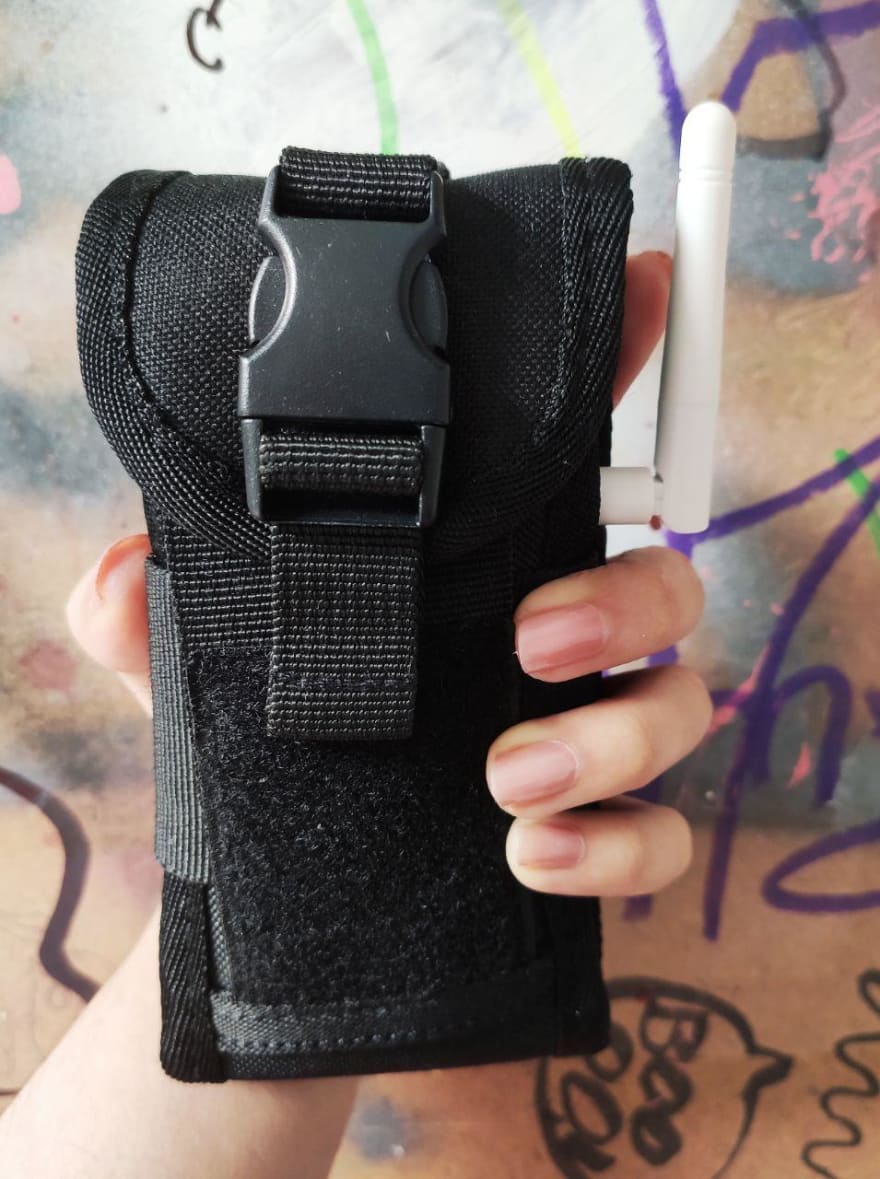
The original WiFi pineapple is a redteam gadget designed by Hak5, an offensive security exclusively brand. There are also Raspberry PI versions, but I’ll use the original one. I’m using a pocket size version.
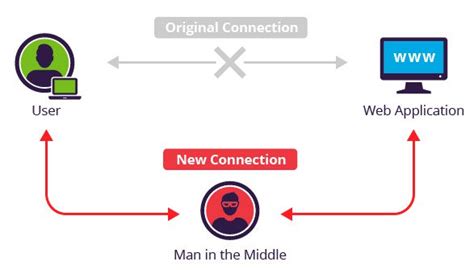
This gadget simulates a router and captures traffic of the ones who connect to it. It aims to assist professionals in MITM (man in the middle) attacks, which consist on steal data of a connection or impersonate someone.
This gadget is a lot of fun I must confess. You can access to the information launching a local web interface, seeing the networks around you, the devices and all. So when you are an user, what you see is an open connection sometimes using a familiar name such as “Starbucks” or something similar, and you can use the Internet (as the Pineaaple is connected to a legit source of Internet connection) so you might not notice you are being watched! Side note, if you try this in a security conference, you might get pranked when trying to do this attack as you might encounter WiFi connections around you named “idiot” or “gotcha”.
In any case be careful out there, and even though an open WiFi is a huge temptation, don’t be gullible. And if, even though, you want to share your WiFi, create a Guest’s WiFi and share a password for it with neighbours.